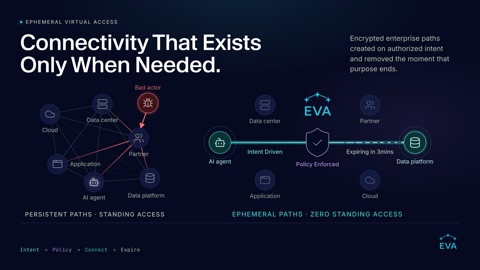
PROVIDENCE, R.I., Sept. 15, 2026 - EVA Networks today emerged from stealth with a new approach to enterprise connectivity built around a simple premise: network access should not exist when it is not needed.
Zero-trust architectures have increasingly reduced standing identity privileges, yet the network
paths connecting applications, clouds, data centers, partners and third parties often remain permanently available. EVA Networks extends the just-in-time model to connectivity itself.
EVA creates encrypted, policy-controlled connections dynamically for an authorized business purpose and automatically removes the underlying network path and connectivity infrastructure when that requirement ends. The approach is designed to reduce unnecessary standing connectivity, attack surface, significant costs, and the operational burden associated with maintaining long-lived tunnels, routes, circuits, and firewall policies.
“Enterprise security has spent years asking who should be allowed to use a connection,” said Dan Sheldon, founder and CEO of EVA Networks. “We started EVA by asking the question: why does the connection need to exist before it is actually required or approved? Temporary business requirements should not create permanent infrastructure.”
Built Around Enterprise Requirements
EVA spent its stealth period developing the platform alongside large organizations operating complex, regulated infrastructure environments rather than launching publicly and then searching for enterprise use cases.
EVA is working with Fortune 50 customers as early adopters.
EVA is designed for use cases including business-to-business connectivity, third-party and vendor access, hybrid and multi-cloud environments, application-to-application communications, just-in-time infrastructure access and emerging agentic AI workloads.
EVA is also extending this model through Ephemeral Agent Paths (EAP), enabling policy-controlled, time-bound connectivity for dynamic workloads and agentic AI systems at the infrastructure layer. As AI agents, automated services and ephemeral compute increasingly need to interact across environments, EAP is designed to help enterprises secure those interactions without leaving standing network paths in place.
Connectivity With a Lifecycle
Rather than treating routes and network relationships as permanent configuration, EVA gives connectivity a defined lifecycle: Intent → Policy → Encrypted Connection → Observation → Expiration